Privacy details are still hard to find in unified AI media APIs. In an August 2026 scan of 17 products, only two published a clear rule for how long they keep your data. This guide shows what to check before you send prompts, images, video, or audio through an API, with Apiframe as the working example.
What a Unified AI Media API Must Protect
A unified AI media API sits between your app, your users, and several model providers. That means your privacy review must cover more than the API endpoint itself.
Start with the data in each request. A text prompt may reveal a campaign plan. An uploaded image may contain a face, a home interior, or a product that has not launched. A music brief can expose a client name or an unreleased brand concept.
Then look at the generated file. The output may carry personal data even when the prompt does not. A request to turn a family photo into a short video, for example, creates a new file tied to an identifiable person.
Your review should cover five kinds of data:
- Input content: prompts, source images, reference video, audio, and metadata.
- Account data: API keys, user IDs, billing records, and support messages.
- Job data: request IDs, model names, status events, errors, and webhook payloads.
- Generated media: files, previews, thumbnails, and CDN URLs.
- Operational logs: IP data, timestamps, usage records, and abuse signals.
Ask who can see each kind of data. Your app may send a request to Apiframe, which then routes it to a selected model provider. That chain raises a basic legal question: who decides how the data gets used, and who only handles it on someone else's instructions. Privacy law calls those two roles the controller and the processor. Your contract should say who acts on your instructions, who may use the data, and what happens if a provider changes.
Apiframe's published Privacy Policy describes TLS encryption for data in transit, AES-256 encryption for data at rest, access controls, and regular security testing. Treat that page as a starting point. If your risk level calls for one, you still need a signed data processing agreement, the contract that sets out how a vendor may handle personal data on your behalf.
That same scan found a wide transparency gap across the category. Public silence does not prove a vendor breaks the law. It does mean you have to ask direct questions instead of reading a page.
Key Takeaway: Review the full data chain, not only the API request. Inputs, outputs, logs, storage, and downstream model access each need a clear owner.
How Data Moves Through Image, Video, and Music Generation
A unified AI media API changes the path your data takes. Instead of one direct call to one model, your app may submit a job to a routing layer, wait for processing, then retrieve a file from hosted storage. The AI image API guide walks through that request and job flow in code.
For an image request, the flow may look like this:
- Your server accepts a prompt and any reference file.
- Your server sends the request with an API key and model parameter.
- The API places the job in a queue and returns a job ID.
- The selected model provider processes the request.
- The API returns a URL to the finished file.
- Your app copies the file into its own approved storage, or deletes it.
Video adds more exposure points because files are larger and jobs take longer. A request may include several reference images, a source clip, motion instructions, or a voice track. Each added input raises the chance that sensitive content reaches a provider or stays in a log. The AI video generation API guide shows how those inputs move through a single job.
Music carries a different risk profile. A lyric draft can contain personal details. A voice reference may count as biometric data in some countries, which brings stricter consent rules. Ask whether the service accepts voice uploads, how it treats those files, and whether the model provider may keep them for training. The AI music API guide explains how those requests are structured.
Webhooks need care too. A webhook should carry a job status or a short-lived reference, not the full media file or a private prompt. Verify the webhook signature if the provider supports one. Store event IDs so a repeated delivery does not bill you twice or publish the same asset twice. The walkthrough on setting up media webhook callbacks covers that handling step by step.
Apiframe runs image, video, and music work as background jobs. You submit a job, receive a job ID, then poll the job or provide a webhook URL. That design keeps long media work out of a normal web request, but it also means your team must map the queue, callback, and storage steps in its data inventory.
The Security page states that API request logs are retained for 90 days for security and debugging. Compare that rule with your own deletion policy. If your app must delete user data within a shorter window, set a separate cleanup job for your own files and local copies.
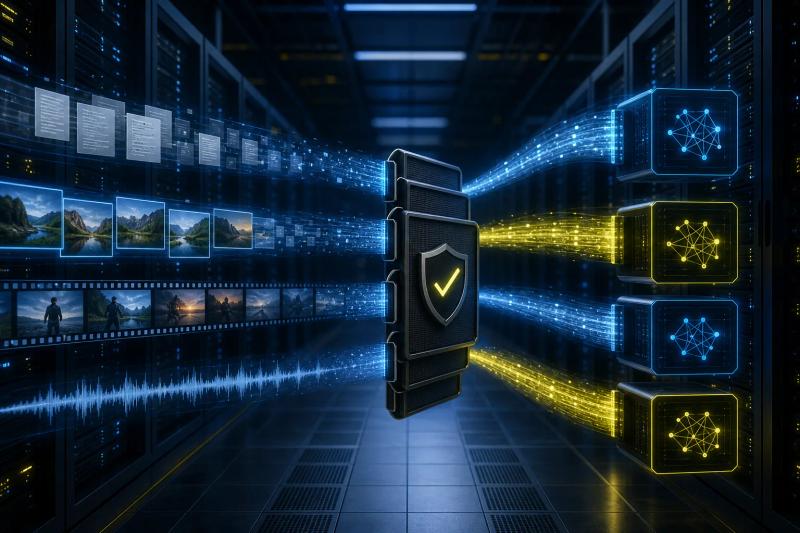
Keep one record of the path for each media type. A diagram can show where data enters, where it waits, which provider handles it, and when each copy disappears. This makes a security review far easier than a vague claim that data is “handled securely.”
Compliance Responsibilities Across Your AI Media Stack
Compliance in a unified AI media API setup is shared. Your API provider can protect its service, but it can't decide why your app collects a user's face, voice, or private files.
You usually own the product decision. That includes why you process the data, the notice shown to users, the legal basis for collecting it, and how you answer access or deletion requests. If a customer uploads a photo for an avatar feature, your product must explain that use in plain language.
The API provider owns the controls described in its contract and policy. Those may cover access limits, incident response, staff access, storage, deletion, and the other vendors it relies on, often called subprocessors. Ask for written answers. A sales call is not a control you can test later.
Model providers add another layer. A unified API may route requests to different vendors based on your model choice. The terms for an image model may differ from those for a video or music model. You need a current list of those vendors and a way to hear about changes.
Write down who owns what for each feature:
- Your team sets the purpose and collects consent where needed.
- The API provider protects its systems and follows the contract.
- The downstream model provider follows its own approved processing terms.
- Your storage provider holds files after they leave the API CDN.
- Your support team handles deletion, export, and complaint requests.
Moderation belongs in the review as well. Ask where harmful content is checked, whether the check happens before generation, and what gets logged when a request fails. The guide to AI content moderation covers those checkpoints. Missing disclosure is a risk signal, not proof of missing controls.
For larger deployments, Apiframe's enterprise page lists a signed DPA, security questionnaire support, and GDPR-ready data handling, with several of those items marked as coming soon rather than available today. Confirm what is in place for your account, data types, and selected models before production use.
Keep your own evidence. Save the policy version, DPA, vendor list, data map, retention settings, and test results. If a customer asks how a generated image was handled, your answer should come from records rather than memory.
Pro Tip: Run a test request with a made-up prompt and a harmless sample file. Trace it through logs, webhooks, CDN storage, and your own database before sending customer data.
Retention, Residency, and Vendor Governance
Retention and residency are separate questions in any unified AI media API compliance review. Retention asks how long data stays. Residency asks where it is stored or processed.
The August 2026 sample found that only two of the 17 products published a retention rule. Recall.ai described configurable retention, including an option to store nothing at all. CometAPI listed indefinite retention and storage across more than one region. The rest of the sample gave no comparable public detail.
Apiframe takes a different approach. Its Privacy Policy and Security page both state that generated content is not kept beyond what is needed to complete your request, unless you turn on an optional storage feature. API request logs are kept for 90 days. Configurable retention, where you set your own storage window, is listed as coming soon. The practical effect is that your app should treat every output as temporary and copy anything it needs into its own storage.
Build deletion around the job ID. When a user deletes a source file, find its related job record, generated media, thumbnail, webhook event, cache entry, and local copy. A database delete alone may leave the file on a CDN or in a worker's temporary folder.
Residency needs the same level of detail. Ask:
- Where does the API receive the request?
- Where does the queue run?
- Where does the model process the input?
- Where does the generated file stay?
- Can support staff access the content from another region?
A multi-region label does not answer every question. It may mean a vendor stores data in more than one place, but it may not tell you which region handles a specific job. Apiframe lists isolated regions and data residency options as coming soon, so ask where your jobs run today. Get the answer in writing if your contract or local law requires a defined location.
Encryption deserves a direct question too. The review dataset held no public encryption details for any of the 17 products. Apiframe is clearer here. Its Privacy Policy and Security page both state TLS encryption in transit and AES-256 encryption at rest, with API keys stored hashed and able to be rotated at any time. Both pages also state that prompts and generated media are never used to train models. Ask who holds the encryption keys, and how backups are covered, when your review needs that level of detail.
Use the Apiframe pricing page to check credit costs and concurrency limits for each plan, and the breakdown of unified AI media API pricing to see how those costs add up per image. A low request price does not help if concurrency limits delay jobs or if your team forgets to export files before they expire.
Vendor governance should continue after launch. Set a review date for policy changes. Track the models enabled for your account. Test deletion once per quarter. If a provider adds a new downstream vendor, pause sensitive workloads until your team approves the change.
A Usable Privacy Review for Apiframe Integrations
A privacy review for an Apiframe integration should end with evidence you can show to a security lead or customer. Start with a small data map, then test the exact workflow your product will run.
1. Classify the input
Mark each field as public, internal, confidential, or personal. Do not send names, emails, face photos, private documents, or unreleased brand files until you know the processing terms for the chosen model.
2. Protect the request path
Keep your Apiframe API key on the server. Never place it in browser code or a mobile app. Limit who can submit jobs, set request quotas, and record your own request ID next to the returned job ID. The post on AI media API security best practices covers key handling and rate limits in more depth.
Use the documented authentication method with the X-API-Key header. The API documentation covers the request shape, job endpoints, and webhook flow, so your team can test the same path it will use in production.
3. Control files and webhooks
Set a clear owner for every generated URL. Copy approved outputs to your own storage when needed. Delete temporary files once the product no longer needs them. Reject unexpected webhook events, and make sure a repeated delivery produces the same result instead of a second charge or a duplicate post.
4. Check model-specific risk
Do not treat all models as equal. A text-to-image prompt may carry less risk than a face reference or a voice sample. Record the selected model, its provider, the data type it receives, and the reason your team approved it. Rights matter as much as privacy here, so check who owns AI-generated output before you ship.
5. Write the user-facing rules
Tell users what your app sends, why it sends it, how long copies remain, and how they can ask for deletion. Add a section on prohibited uploads if your workflow accepts public submissions. Give your support team a way to find the related job without exposing the media to staff who don't need access.
Finally, ask Apiframe for the documents your risk review needs. Public pages state the baseline controls, but a production review may also need a DPA, a list of downstream vendors, incident terms, and region commitments. Some of those are still on the roadmap, so ask where each one stands today and keep the answer tied to the account and the date you approved it.
FAQ
What is a unified AI media API?
A unified AI media API gives your app one interface for several image, video, or music models. You send requests through one authentication and job flow instead of building a separate integration for every provider. The privacy trade-off is that one request may pass through a routing layer and a downstream model provider.
Is Apiframe GDPR compliant?
Not formally, at the time of writing. Apiframe lists GDPR-ready data handling and a signed DPA on its enterprise page as coming soon, alongside SOC 2 Type II. Ask the team where each item stands today, then confirm retention, deletion, and residency terms for your use case. A public compliance statement is not a substitute for reviewing your own data, account, and selected models.
How long does Apiframe keep generated media?
Apiframe states that generated content is not kept beyond what is needed to complete your request, unless you turn on an optional storage feature. API request logs are kept for 90 days. Export anything you need to keep, then set your own deletion rules for the copy your app stores.
Does an AI media API encrypt uploaded files?
Do not assume encryption details when a vendor does not publish them. Ask about encryption in transit, encryption at rest, key access, and backups. Apiframe publishes both sides: TLS for data in transit and AES-256 for data at rest, with API keys stored hashed. Your security review should still confirm the scope and the controls that apply to each downstream model.
What should I ask an AI media API vendor?
Ask who processes each media type, where jobs run, how long files and logs remain, whether data trains models, and how deletion works. Also request a vendor list, incident terms, access controls, moderation details, and a DPA when required. Put the important answers in the contract rather than relying on informal statements. The checklist on how to choose an AI media API covers the questions worth asking at the same time.
Conclusion
Choose a unified media API that gives your team a clear data path and written controls. Apiframe is a sensible place to start because its public pages state TLS and AES-256 encryption, 90-day log retention, and no model training on your prompts or outputs. Run a test job, trace every copy, then ask for the contract terms before production. If your workload includes personal or regulated media, start that conversation with the enterprise team.